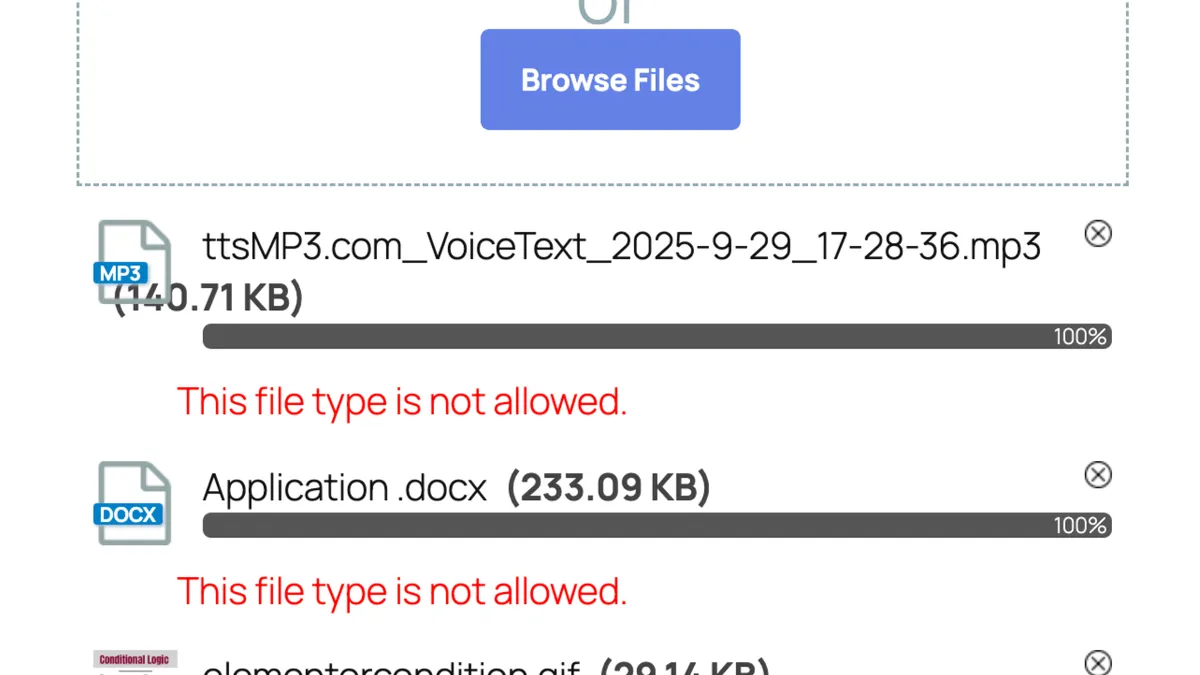

A critical file-upload vulnerability has been disclosed in the third-party Drag and Drop File Upload for Elementor Forms WordPress plugin, potentially allowing unauthenticated attackers to upload dangerous files to vulnerable websites.
The issue, tracked as CVE-2026-18351, affects versions up to and including 1.6.0. Patchstack’s security advisory lists version 1.6.1 as patched and recommends updating immediately.
The flaw is in this separate file-upload add-on, not Elementor core or Elementor Pro itself. That distinction matters for small businesses using Elementor forms to collect CVs, quote attachments, artwork, support documents or other customer files: updating Elementor Pro alone does not update this add-on.
The official WordPress.org plugin listing currently shows version 1.6.1 and more than 1,000 active installations. Site owners should check the Plugins screen and confirm that the add-on is running 1.6.1 or later. If it is no longer needed, removing an unused upload extension is safer than leaving an outdated component active.
Businesses that had an affected version exposed should also review recent uploads, unexpected executable files and unfamiliar administrator accounts. If there are signs that a site may already have been compromised, our guide on what to do after a WordPress website is hacked explains the immediate recovery steps.
For firms that do not manage plugin updates themselves, regular WordPress maintenance and support should include plugin inventory checks as well as routine updates. File-upload extensions deserve particular attention because they accept data directly from website visitors.
The authoritative sources reviewed do not establish that CVE-2026-18351 is already being exploited at scale. The practical action is therefore to patch promptly and check exposed sites, rather than assume that every affected installation has already been compromised.